BeginnerVendor-neutral6 modulesCertificate
About this course
An AI agent is a program that reads its inputs, decides what to do, and calls tools to do it, round and round until the job is done. That loop is what makes agents useful, and it is also why the security model you already know stops fitting. An email can carry an instruction. A tool grant can turn one paragraph of text into a refund. Three copies of the same assistant can share one key that nobody can trace.
This course teaches the concepts you need to reason about that, in the order you would use them to secure an agent for real: understand the risk, work out who is calling, limit what it can do, keep credentials out of its hands, and watch what happens in production. Every lesson follows one running story, a travel company whose support assistant issued forty-one refunds over a weekend, and each module returns to it with one more control in place.
It is built for people who work with agents rather than people who build security products: developers adding agents to a product, platform and security engineers who need to assess or govern them, and technical product managers and architects making build-or-buy calls. Everything is explained with diagrams, plain-language rules and pseudo-code. Lessons name open standards such as OAuth, OIDC, OpenTelemetry and the OWASP guidance, and never a vendor or an SDK, so what you learn holds up whichever tools your team ends up using.
Each module pairs short videos with interactive exercises you play in the browser, a reading, and a graded quiz. The last module closes with a case study: a hijacked support agent's audit trail, which you work through end to end. Passing the quizzes and the case study earns the course certificate.
What you will be able to do
- ✓ Describe the attack surface AI agents create: prompt injection and the four doors it comes through, over-privileged tools, data disclosure, credential sprawl and shadow agents.
- ✓ Explain how agents get verifiable identities and why every agent should be a known principal behind one enforcement point.
- ✓ Apply least privilege to agent tool access, and read and write simple default-deny authorization rules.
- ✓ Recognise unsafe credential handling and explain delegation patterns where the agent never holds the user's secret.
- ✓ Use audit logs and traces to reconstruct what an agent did, and outline the first steps to contain one that is misbehaving.
The modules
- 01 Welcome and course orientation
What you are signing up for, and the story the whole course follows. - 02 AI agents and what can go wrong
Why agents break the security model you already know. - 03 Agent identity and authentication
Who is this agent, and how do we know? - 04 Least privilege and authorization
What is this agent allowed to do, and who said so? - 05 Keeping secrets away from agents
How an agent acts for a user without holding their credentials. - 06 Watching agents and responding to incidents
What the agent did, and how to stop it.
About eleven hours in all, paced over five weeks at two to three hours a week. Everything is self-paced, so you can go faster.
Requirements
Know what an API is and have seen a login flow. That is all. You do not need a security background, and there is no coding: every example is a diagram, a plain-language rule or pseudo-code. A modern browser is enough for the exercises.
Course staff
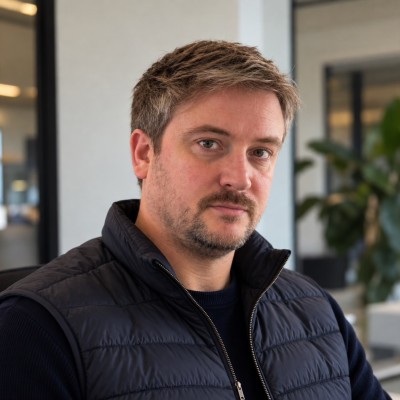 Peter Kelly Chief Technology Officer, Tigera
Peter opens the course and sets out why agent security needs its own discipline, drawing on Tigera's work securing agents and the networks they run on.
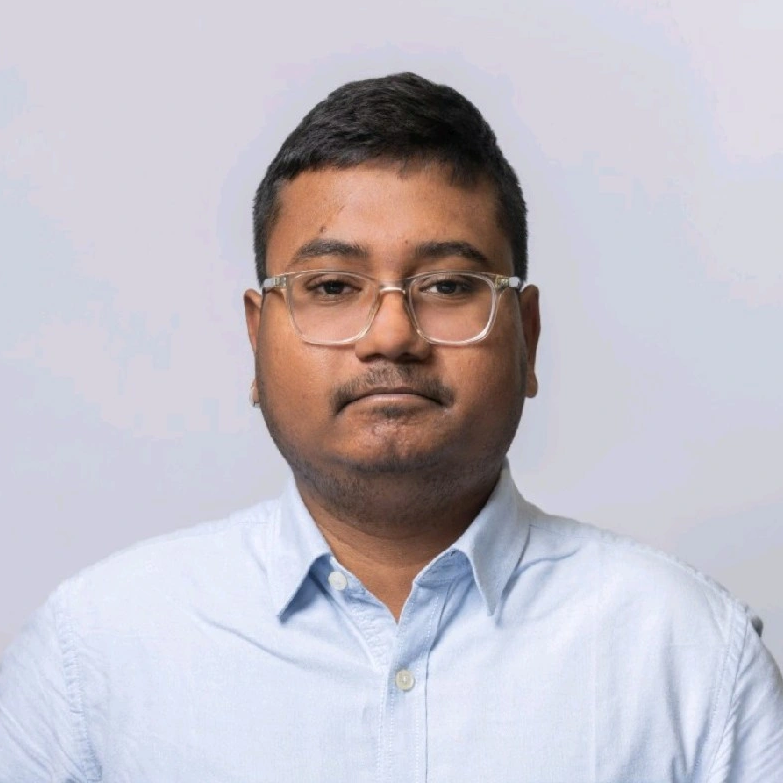 Alister Baroi Technical Evangelist, Tigera
Alister teaches the five content modules and built the course's interactive exercises. He works on how AI agents are secured in production and writes and speaks about agent security for developers who are meeting it for the first time.
Frequently asked questions
Do I need to know how to code?
No. The course explains everything with diagrams, plain-language rules and pseudo-code. The exercises run in your browser and ask you to reason, not to type code.
Does the course use a particular product or framework?
No. It names open standards, such as OAuth, OIDC and OpenTelemetry, and never a vendor or an SDK, so it applies whichever agent framework or security tools your team uses.
How is it graded?
Each content module ends with a multiple-choice quiz, and the last module adds a case study. Quizzes have an 80 percent pass mark and can be retaken. The interactive exercises are practice and count towards progress, not the grade.
Is there a certificate?
Yes. Passing every graded quiz and the case study earns the Tigera Academy certificate for this course.
What comes after this course?
This is course 1 of the four-course AI Agent Security Expert series. The later courses pick up the hands-on and Kubernetes material this one deliberately defers: implementing agent identity, writing real policies, and running the controls in production.
What browser should I use?
A current version of Chrome, Firefox, Safari or Edge. The exercises need JavaScript enabled.